Auto-generate compliant policies, track versions, and enforce standards like ISO, NIST, and GDPR—all from one collaborative dashboard.

Track versions, approvals, and expiry dates stay audit-ready from draft to retirement.

Apply policy rules instantly across departments, platforms, and business units.

Simulate real-world threats and measure how well your controls withstand them—quantifying audit resilience.

Map internal policies to ISO, NIST, GDPR, and SOC 2—no manual cross-referencing needed.

Get full traceability of every action and a live score of your policy maturity.
CyberScore integrates with your existing tools—M365, Wazuh, AWS, and more—to validate your security posture in real time. No setup guesswork. Just plug in, scan, and score.
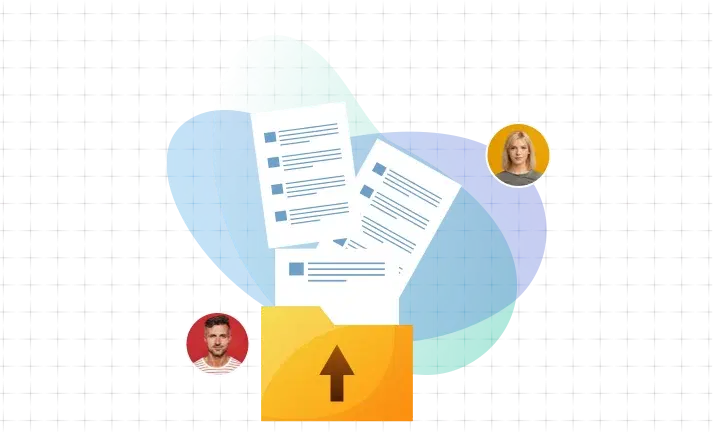
Start with a policy template or build from scratch. Assign roles and share instantly with team members or auditors.
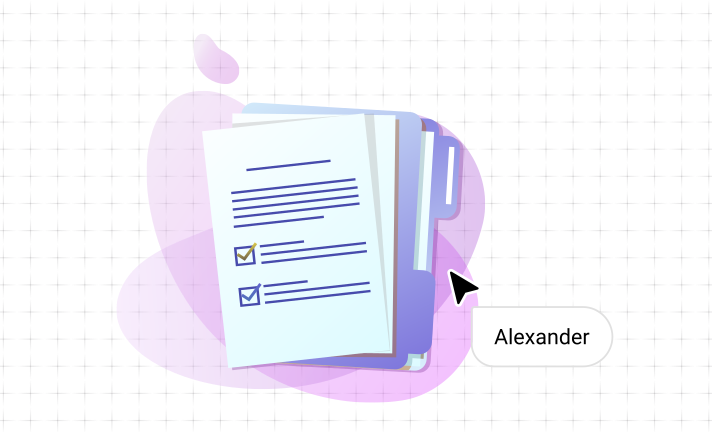
Collaborate in real time co-author, comment, and track changes. Set review cycles and approval workflows with full version control.
Empower your teams to create, review, and enforce policies—without the manual chaos. GovernAI simplifies lifecycle management, aligns with global standards, and keeps your organization audit-ready.
"GovernAI turned our scattered policy drafts into a single, living system. Now every edit, comment, and approval is traceable—and our audits run smoother than ever."
"We used to chase policies across departments. GovernAI gave us version control, task tracking, and auditor-ready packages—all in one dashboard."
"GovernAI doesn't just store policies—it understands them. From ISO to GDPR, it auto-maps our documents and flags gaps before we even start the review."